Cryip
  • Home
  • Crypto News Today
  • Research & Analysis
  • Learn Crypto
No Result
View All Result
Cryip
  • Home
  • Crypto News Today
  • Research & Analysis
  • Learn Crypto
No Result
View All Result
Cryip
No Result
View All Result
Home Crypto News Today Security & Hacks

Uniswap V4 Router04 Exploited: $42,100 Drained in On-Chain Attack

Uniswap V4 Router04 contract has resulted in a $42,100 theft on the Ethereum network. The exploit targeted permissions within the z0r0z.eth deployed contract, successfully draining assets from a victim’s wallet.

Saravana Kumar Mahendran by Saravana Kumar Mahendran
March 3, 2026
in Security & Hacks
0 0
Uniswap V4 Router04 Exploited
Share on FacebookShare on Twitter
MakeCryipCryippreferred onGoogle

An exploit in the Uniswap V4 Router04 contract on the Ethereum network has resulted in a loss of approximately $42,100. The breach, which involved a contract deployed by z0r0z.eth, has raised immediate concerns regarding the safety of experimental routing logic in the Uniswap V4 ecosystem. According to blockchain data, a specific vulnerability within the Router04 contract allowed unauthorized access to the victim’s funds, highlighting the inherent risks associated with early-stage “Hooks” and custom routers on the mainnet.
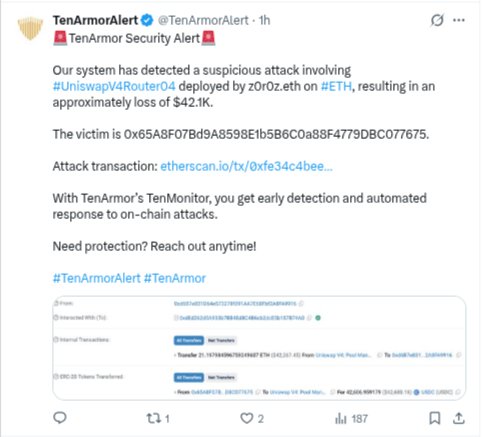
Uniswap V4 Router04 Exploited

Attack Details (On-Chain Data):

Metric Details
Victim Address 0x65A8F07Bd9A8598E1b5B6C0a88F4779DBC077675
Network Ethereum Mainnet (ETH)
Assets Stolen ~21.19 ETH and USDC stablecoins
Estimated Loss $42,100 USD
Transaction Hash 0xfe34c4beee447de536bbd3d613aa0e3aa7eeb63832e9453e4ef3999924ab466a

Technical Deep Dive: How the Exploit Occurred

Security researchers believe the exploit was made possible through a flaw in how the Router04 contract handles user permissions and interactions with the Uniswap V4 Pool Manager.

  • Approval Exploitation: The victim had previously granted the Router04 contract permission (approval) to spend their tokens for swaps. In a standard scenario, the contract only moves funds as part of a legitimate user-initiated trade. However, the attacker identified a logical flaw that allowed them to “trigger” the contract into moving the victim’s funds to an external address controlled by the hacker.

  • Logical Call Flaw: Preliminary analysis suggests the router failed to properly validate the caller’s identity during specific function executions. By injecting a malicious “call,” the attacker tricked the router into thinking it was executing a valid swap, while it was actually draining the user’s wallet.

  • V4 Hook Complexity: The introduction of “Hooks” in Uniswap V4 allows for highly customizable trades, but it also increases the attack surface. In this instance, the interaction between the router’s logic and the pool’s state seems to have lacked the necessary “guardrails” to prevent unauthorized fund withdrawals.

A Crucial Lesson in “Security Hygiene”

This incident serves as a stark reminder of the dangers of “Unlimited Approvals.” In the DeFi world, most users grant contracts permission to spend an infinite amount of a specific token to simplify future trades. However, if that contract—or a router connected to it is compromised, hackers can drain every token associated with that approval.

To mitigate such risks, technical experts recommend a “Limited Approval” approach: only granting permission for the exact amount of a single transaction. Furthermore, users are urged to use tools like Revoke.cash or Etherscan’s approval checker to regularly clear out old or unnecessary permissions, ensuring that even if a contract is exploited in the future, their assets remain out of reach.

This exploit is part of a growing trend of DeFi vulnerabilities; for instance, the February 2026 crypto security report highlights that over $23 million was lost across various incidents last month alone. Staying informed about these recurring threats is the first step toward maintaining a secure on-chain presence.

Disclaimer: Cryip's content is strictly for educational and informational purposes and does not constitute financial, legal, or investment advice. Cryptocurrency involves significant risk, and readers assume full responsibility for their own financial decisions. Asset references are never endorsements.

To make complex crypto topics accessible to readers at all experience levels, our team uses AI tools strictly to refine language, correct grammar, and simplify terminology. AI is never used to draft facts, source information, or form conclusions. Every article is fact-checked and approved by a human editor before publication. Read our full AI Use & Content Policy.
Tags: Crypto Hacks
Saravana Kumar Mahendran

Saravana Kumar Mahendran

Saravana Kumar Mahendran is a crypto security analyst and blockchain researcher at Cryip, focusing on DeFi protocol exploits, Web3 security systems, and on-chain investigation. His research applies OSINT and fact-checking methodology to security incidents, drawing on certifications in cybersecurity and data analytics (LinkedIn Learning), and DeFi deep-dive training (Binance Academy). His work has been cited by Sherlock, Rekt.news, and Halborn Security.

Related Posts

More Markets on Flow EVM Becomes Third DeFi Lending Exploit in Five Days
Security & Hacks

More Markets on Flow EVM Becomes Third DeFi Lending Exploit in Five Days

by Saravana Kumar Mahendran
August 31, 2026

More Markets, a lending protocol built on Flow EVM, lost about $9.3 million on Sunday after an attacker used a...

Read moreDetails
Fogo Foundation Says Wallet Breach Sent 400M FOGO Tokens to Unknown Attacker

Fogo Foundation Says Wallet Breach Sent 400M FOGO Tokens to Unknown Attacker

August 29, 2026
Avici Confirms $500,859 Refund to 1,685 Users After Rain Contract Flaw

Avici Confirms $500,859 Refund to 1,685 Users After Rain Contract Flaw

August 29, 2026
Sandbox’s $1 trillion in phantom SAND is still frozen. The real bridge hack cost under $700,000.

Sandbox’s $1 Trillion Phantom SAND Frozen as Real Hack Cost Hits $700K

August 28, 2026
Moonwell Hit by Third Exploit in Nine Months After Attacker Drains Millions in cbBTC

Moonwell Hit by Third Exploit in Nine Months After Attacker Drains Millions in cbBTC

August 27, 2026
Three Cosmos EVM Chains Halt After a Flaw Cosmos Labs Already Called Fixed

Three Cosmos EVM Chains Halt After a Flaw Cosmos Labs Already Called Fixed

August 25, 2026
Kylie Jenner’s X Account Hacked to Push a Pump.fun Token

Kylie Jenner’s X Account Hacked to Push a Pump.fun Token

August 25, 2026
Next Post
Five Bells Raises Seed Round to Build Bitcoin-Based Post-Trade Infrastructure

Five Bells Raises Seed Round to Build Bitcoin-Based Post-Trade Infrastructure

Google security update

Google Chrome Security Update High-Severity Gemini AI Vulnerability Patched

Recommended

  • All
  • Crypto News Today
Coinbase Completes Deribit Integration, Unveils "Coinbase Global Exchange"

Coinbase Completes Deribit Integration, Unveils “Coinbase Global Exchange”

October 9, 2026
AVAX One Technology Eliminates $14.9 Million in Debt, Extends Share Buybacks in Q3 Update

AVAX One Technology Eliminates $14.9 Million in Debt, Extends Share Buybacks in Q3 Update

October 9, 2026
Figure Technology Solutions Reports Preliminary Q3 2026 Marketplace Volume of $5.12 Billion

Figure Technology Solutions Reports Preliminary Q3 2026 Marketplace Volume of $5.12 Billion

October 9, 2026
FDUSD Issuer First Digital to Go Public on Nasdaq via SPAC Merger With CSLM Digital Asset Acquisition Corp III

FDUSD Issuer First Digital to Go Public on Nasdaq via SPAC Merger With CSLM Digital Asset Acquisition Corp III

October 9, 2026
SRX Global Commits $1.5 Million to Launch AI-Powered Digital Asset Hedging ETFs

SRX Global Commits $1.5 Million to Launch AI-Powered Digital Asset Hedging ETFs

October 9, 2026
OpenWorld Signs Up-to-$130 Million Deal to Tokenize AI Firm BeyondAI's Patents

OpenWorld Signs Up-to-$130 Million Deal to Tokenize AI Firm BeyondAI’s Patents

October 9, 2026
Bullish Discloses $48.6 Billion in September Trading Volume in Monthly Metrics Report

Bullish Discloses $48.6 Billion in September Trading Volume in Monthly Metrics Report

October 9, 2026
PowerCompute Expands Mississippi Mining Site to 11 Megawatts Under New TVA Tariff

PowerCompute Expands Mississippi Mining Site to 11 Megawatts Under New TVA Tariff

October 9, 2026

Cryip focuses on crypto research and on-chain analysis, supported by coverage of markets, regulation, security events, and blockchain ecosystems.

Recent Posts

  • Winklevoss Group Files S-1 for a Zcash ETF Under Ticker “WINK”
  • Coinbase Completes Deribit Integration, Unveils “Coinbase Global Exchange”
  • AVAX One Technology Eliminates $14.9 Million in Debt, Extends Share Buybacks in Q3 Update

Categories

  • AI News
  • Data & Dashboards
  • DeFi Basics
  • Investing Basics
  • Market & Price
  • Market Updates
  • On-Chain Analysis
  • OpSec
  • Policy & Regulation
  • Post Mortems
  • Press Release
  • Reports
  • Research & Analysis
  • Scams & Fraud
  • Security & Hacks
  • Stablecoins
  • Tokenomics
  • Uncategorized
  • VC & Funding
  • Wallets & Custody

Company

  • About Us
  • Contact Us
  • Editorial Standards & Integrity
  • Our Team
  • Privacy Policy
  • Review Methodology
  • Terms and Conditions
  • Trust, Disclosures & Independence

© 2026 Cryip - Research-Driven Crypto Analysis & News by Hashlays.

Welcome Back!

Login to your account below

Forgotten Password?

Retrieve your password

Please enter your username or email address to reset your password.

Log In

Add New Playlist

No Result
View All Result
  • Home
  • Crypto News Today
  • Research & Analysis
  • Learn Crypto

© 2026 Cryip - Research-Driven Crypto Analysis & News by Hashlays.

This website uses cookies. By continuing to use this website you are giving consent to cookies being used. Visit our Privacy and Cookie Policy.